
Popular
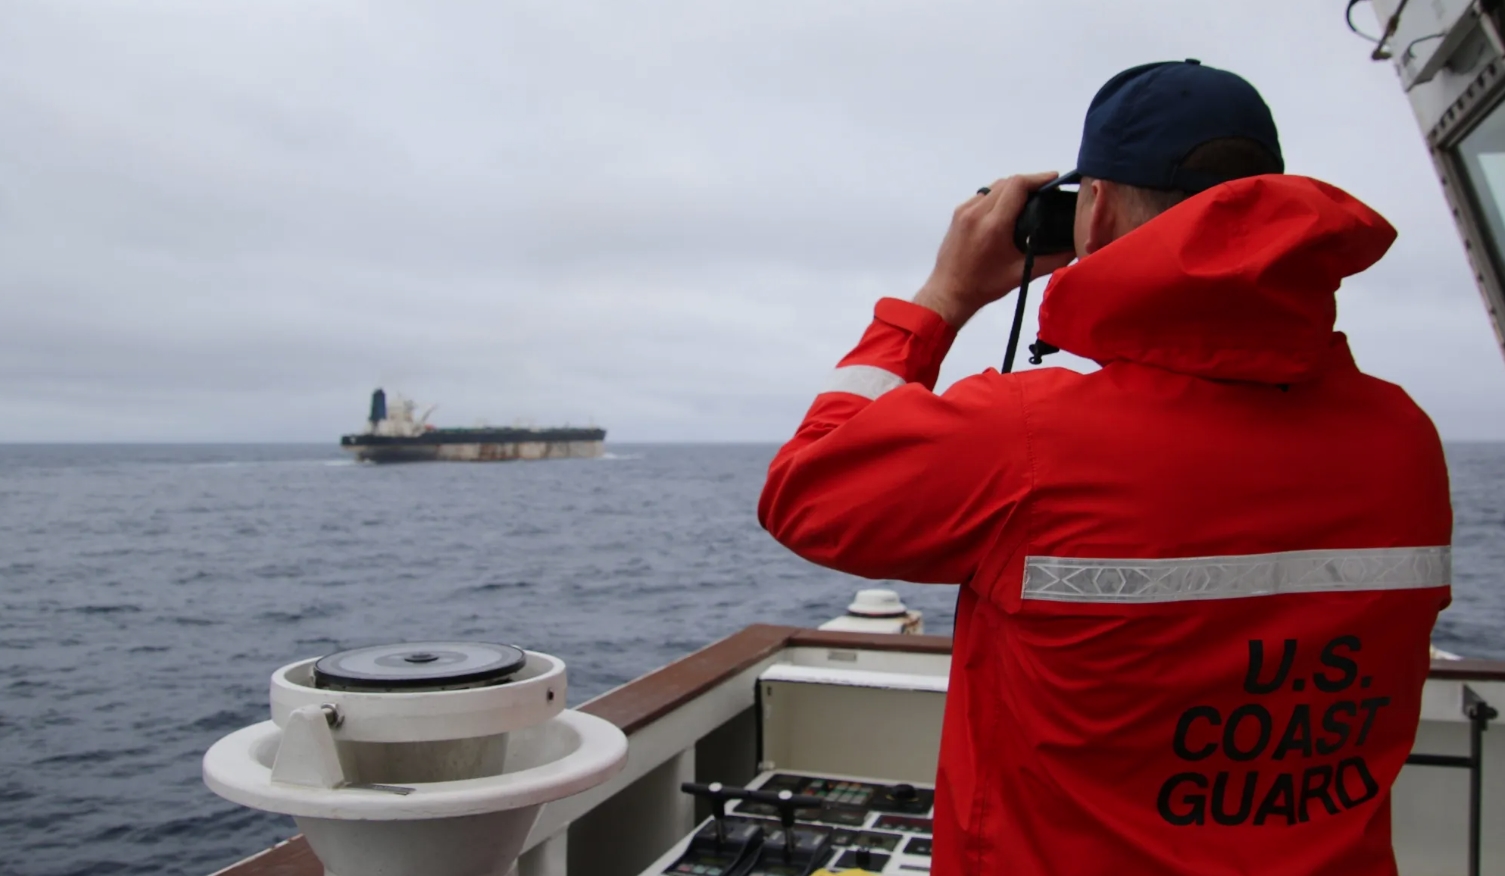
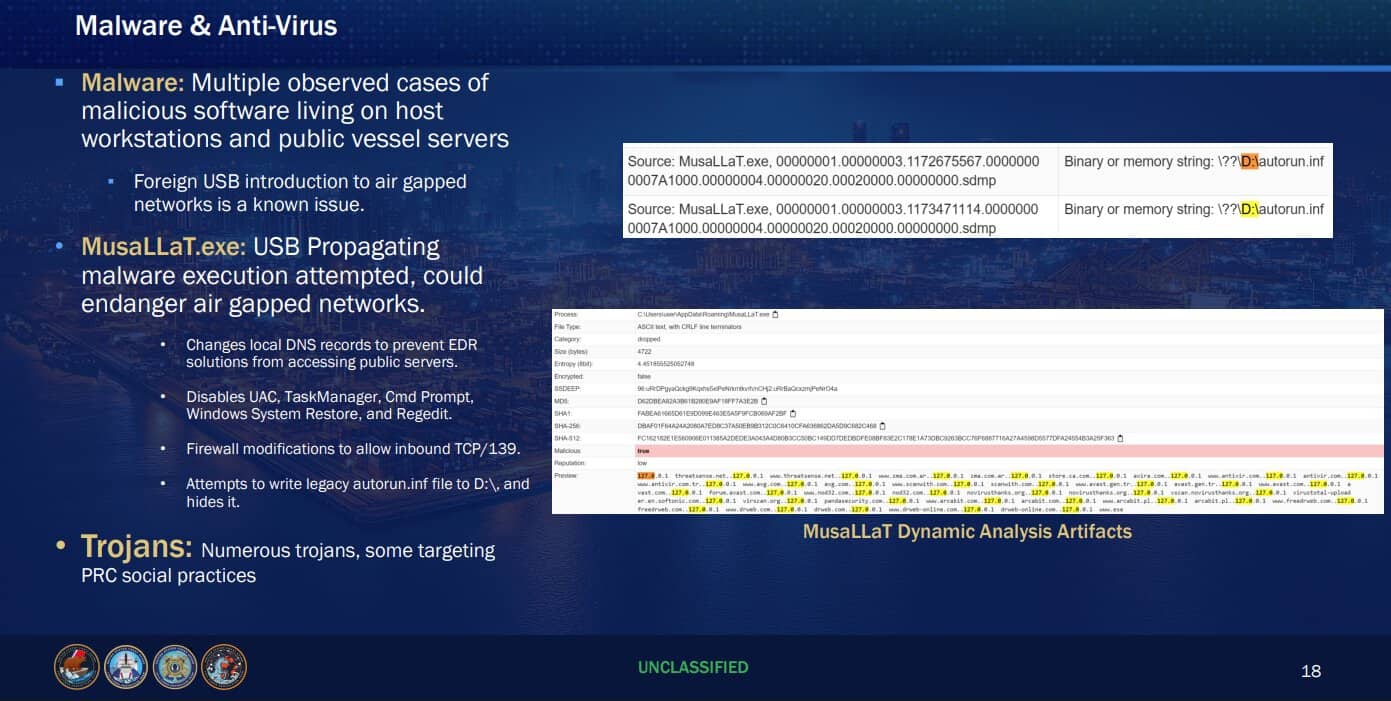
U.S. Coast Guard experts have revealed the technical methods that Russian shadow fleet vessels use to conceal their activities.
The presentation was given at the DEF CON 34 conference, and an analysis of it was prepared by the InformNapalm community.
These vessels actively use methods to spoof data from the Automatic Identification System (AIS).
Several transponders, tools for spoofing coordinates, means of remote access to ship computers, and tools for quickly forging documents were also found on board the vessels.
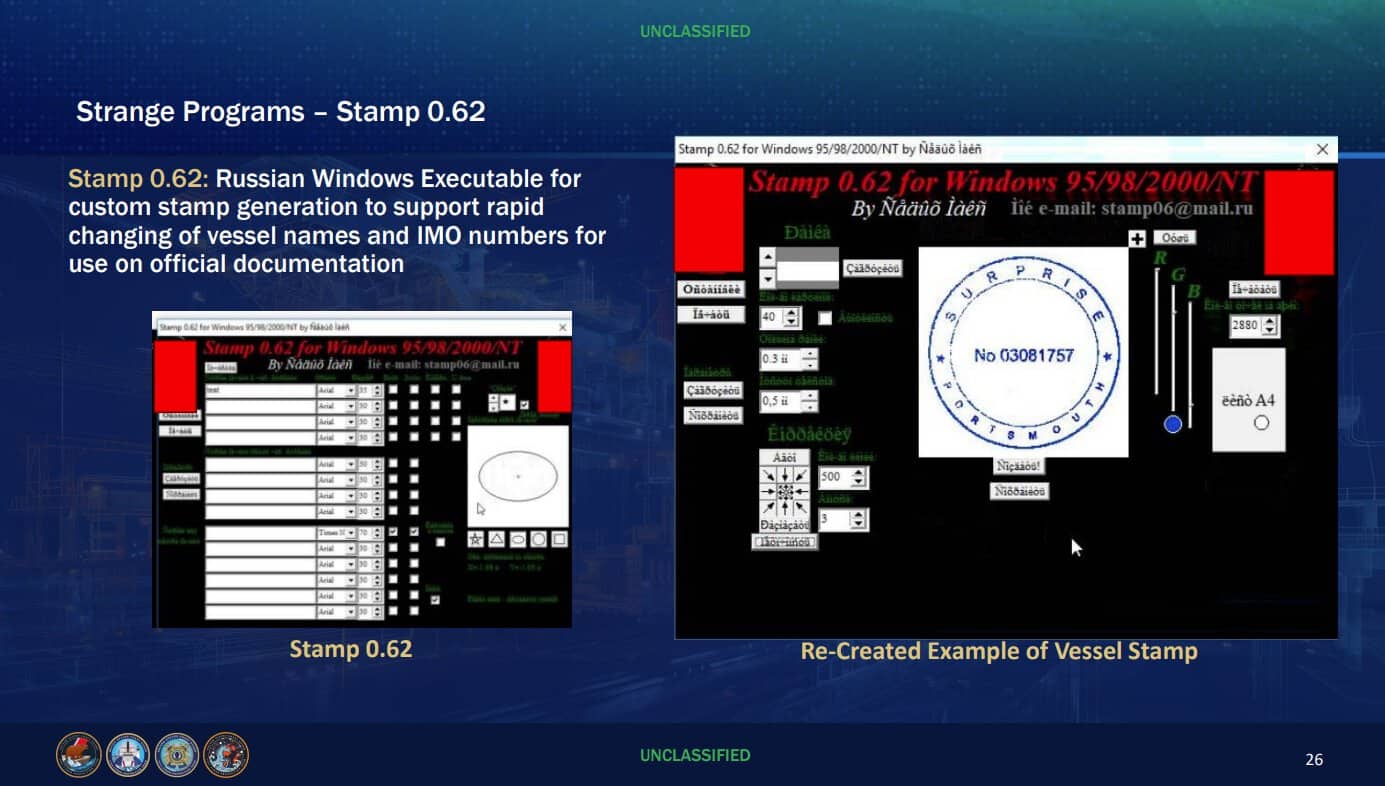
“One of the most revealing finds is the Russian program Stamp 0.62 for Windows. It allows for the rapid generation of images of ship seals in the event that the ship’s name or IMO number is changed in documents,” InformNapalm reports.
One of the main concealment tools is related to the AIS system, which vessels use to transmit their names, coordinates, and other data.
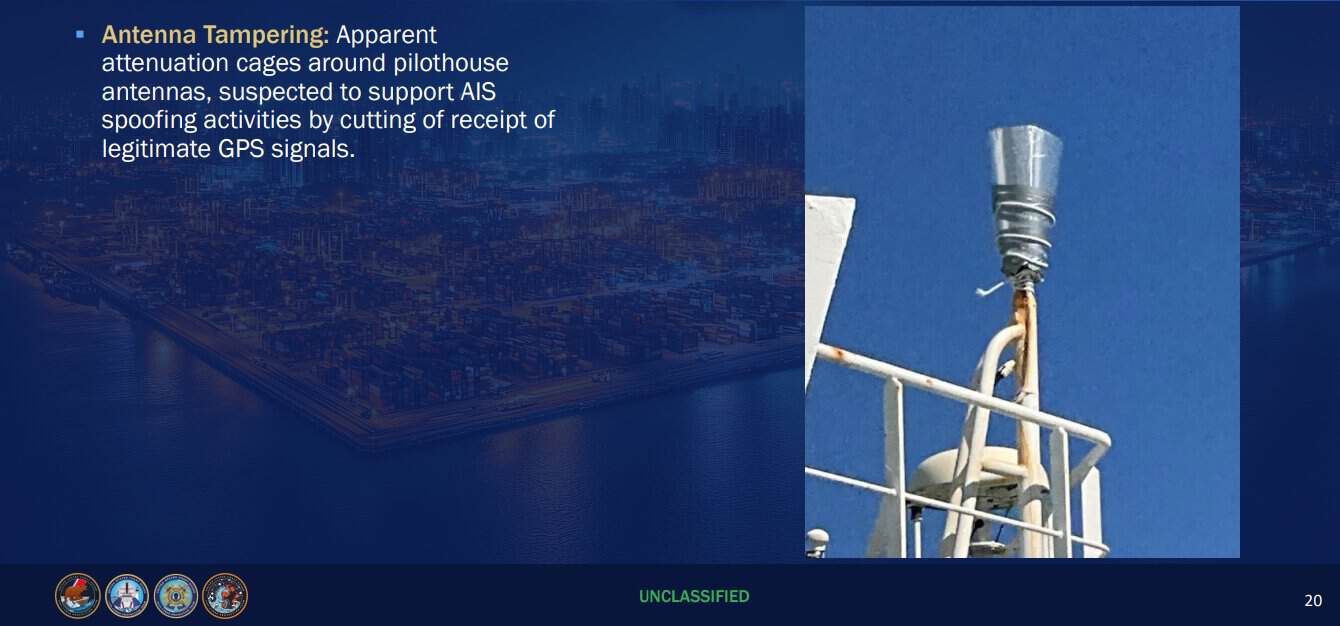
On some tankers, researchers have detected multiple transponders that can be switched between, as well as equipment and software for transmitting false GPS coordinates.
In simpler cases, the crew could physically restrict the antenna’s operation and thus stop the signal from being transmitted.
At the same time, the onboard IT infrastructure is often quite rudimentary.
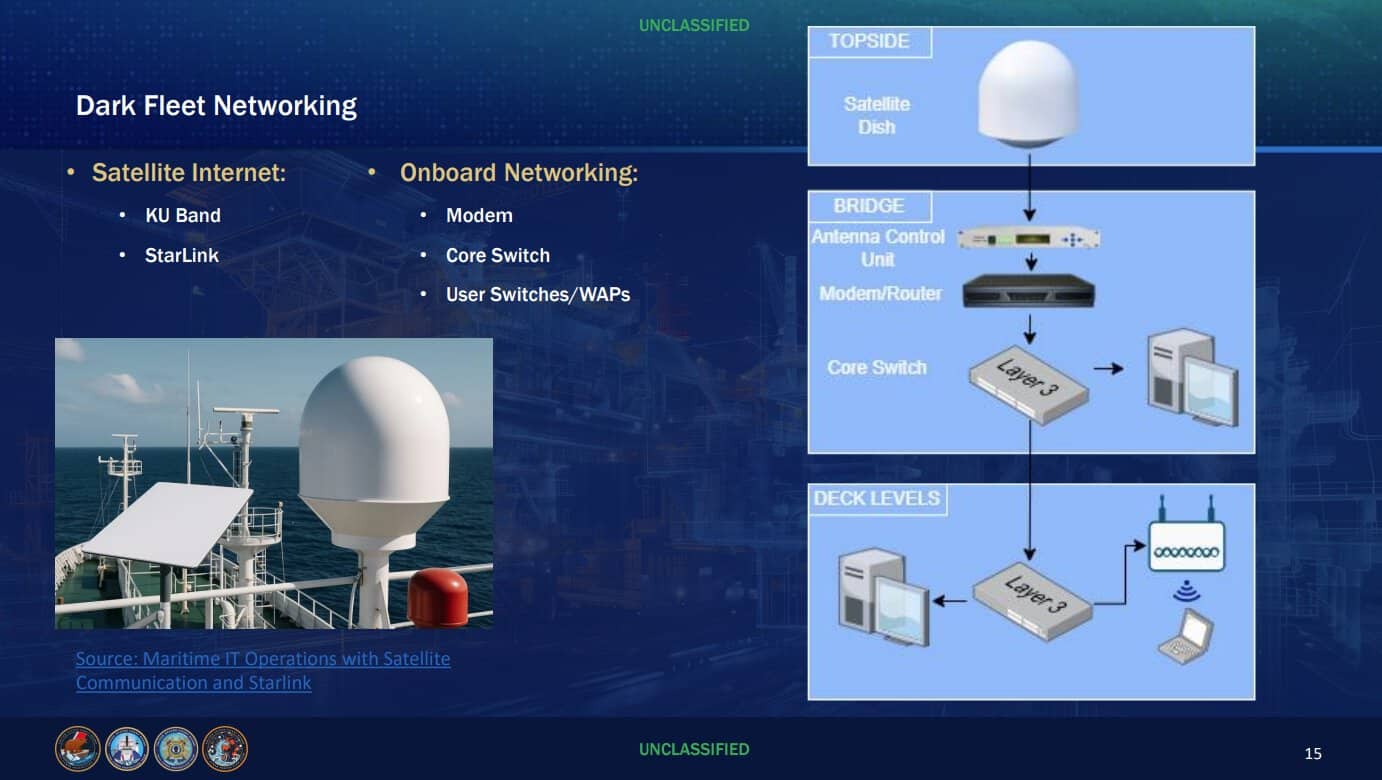
Researchers found pirated navigation programs, software from torrent forums, and common remote access tools such as AnyDesk, TeamViewer, and ScreenConnect, which could operate without the crew’s authorization.
During some operations, external operators attempted to remotely erase data from the ship’s systems after the vessel had already been detained. They use off-the-shelf digital tools for this purpose, so changing a vessel’s name, flag, or identity may be accompanied not only by a false AIS signal but also by a corresponding set of documents.
Currently, vessels from Russia’s shadow fleet are being actively intercepted by European Union forces. Recently, the Italian Navy intercepted an oil tanker from Russia’s shadow fleet in the Mediterranean Sea.
Підтримати нас можна через:
Приват: 5169 3351 0164 7408 PayPal - [email protected] Стати нашим патроном за лінком ⬇
Subscribe to our newsletter
or on ours Telegram
Thank you!!
You are subscribed to our newsletter